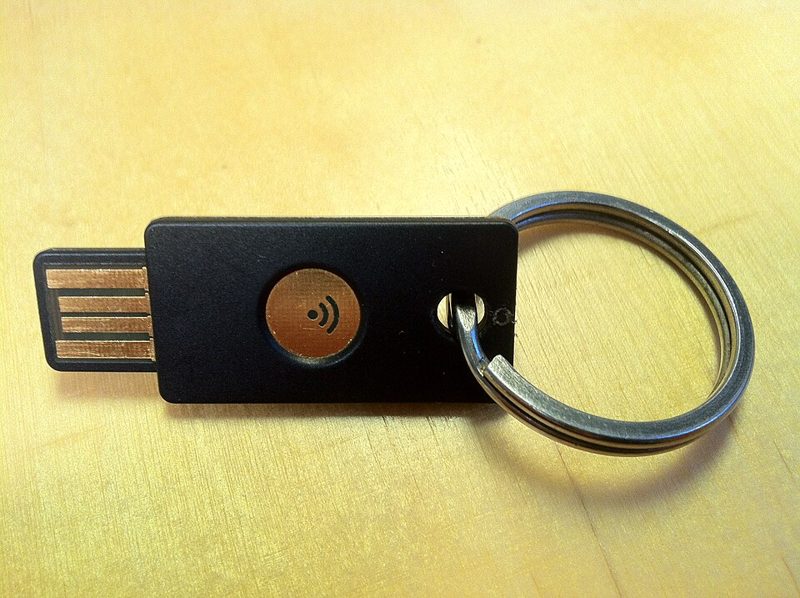
Yes. Passkeys are generally safer than passwords because they use public-key cryptography: the website stores only a public key, while the private key stays on your phone, computer, password manager, or hardware security key and is unlocked with your fingerprint, face, PIN, or screen-lock pattern. There is no shared secret to guess, reuse across sites, or steal in a database breach, and each passkey is tied to the real website or app it was created for, which makes it resistant to phishing.
The FIDO Alliance, which maintains the standard, says a passkey on its own is more secure than a password combined with a one-time code or a phone approval prompt, since both of those can still be phished. The main remaining risk is the security of the device or account that stores your passkeys, so keep that device locked and its account protected.
Source: FIDO Alliance, “Passkeys”.
Image: YubiKey hardware security key, photo by Dennis (CC0), via Wikimedia Commons.